Bank Compliance & Risk Readiness
Cicrim helps banks and credit unions strengthen regulatory readiness across cybersecurity, vendor risk, governance, model risk management, and operational controls. We reduce exam friction by building durable documentation, control evidence, and repeatable compliance operations, with practical AI where it fits.
Bank Compliance
A comprehensive approach to bank compliance and risk, designed for community and regional institutions
Cicrim partners with banks and credit unions to streamline regulatory execution and strengthen control evidence across cybersecurity, third-party risk, governance, internal controls, and model risk. We help you move from “compliance as a fire drill” to consistent, repeatable operations, supported by modern workflows and practical automation.
Beyond checking the box: Build compliance that improves operations
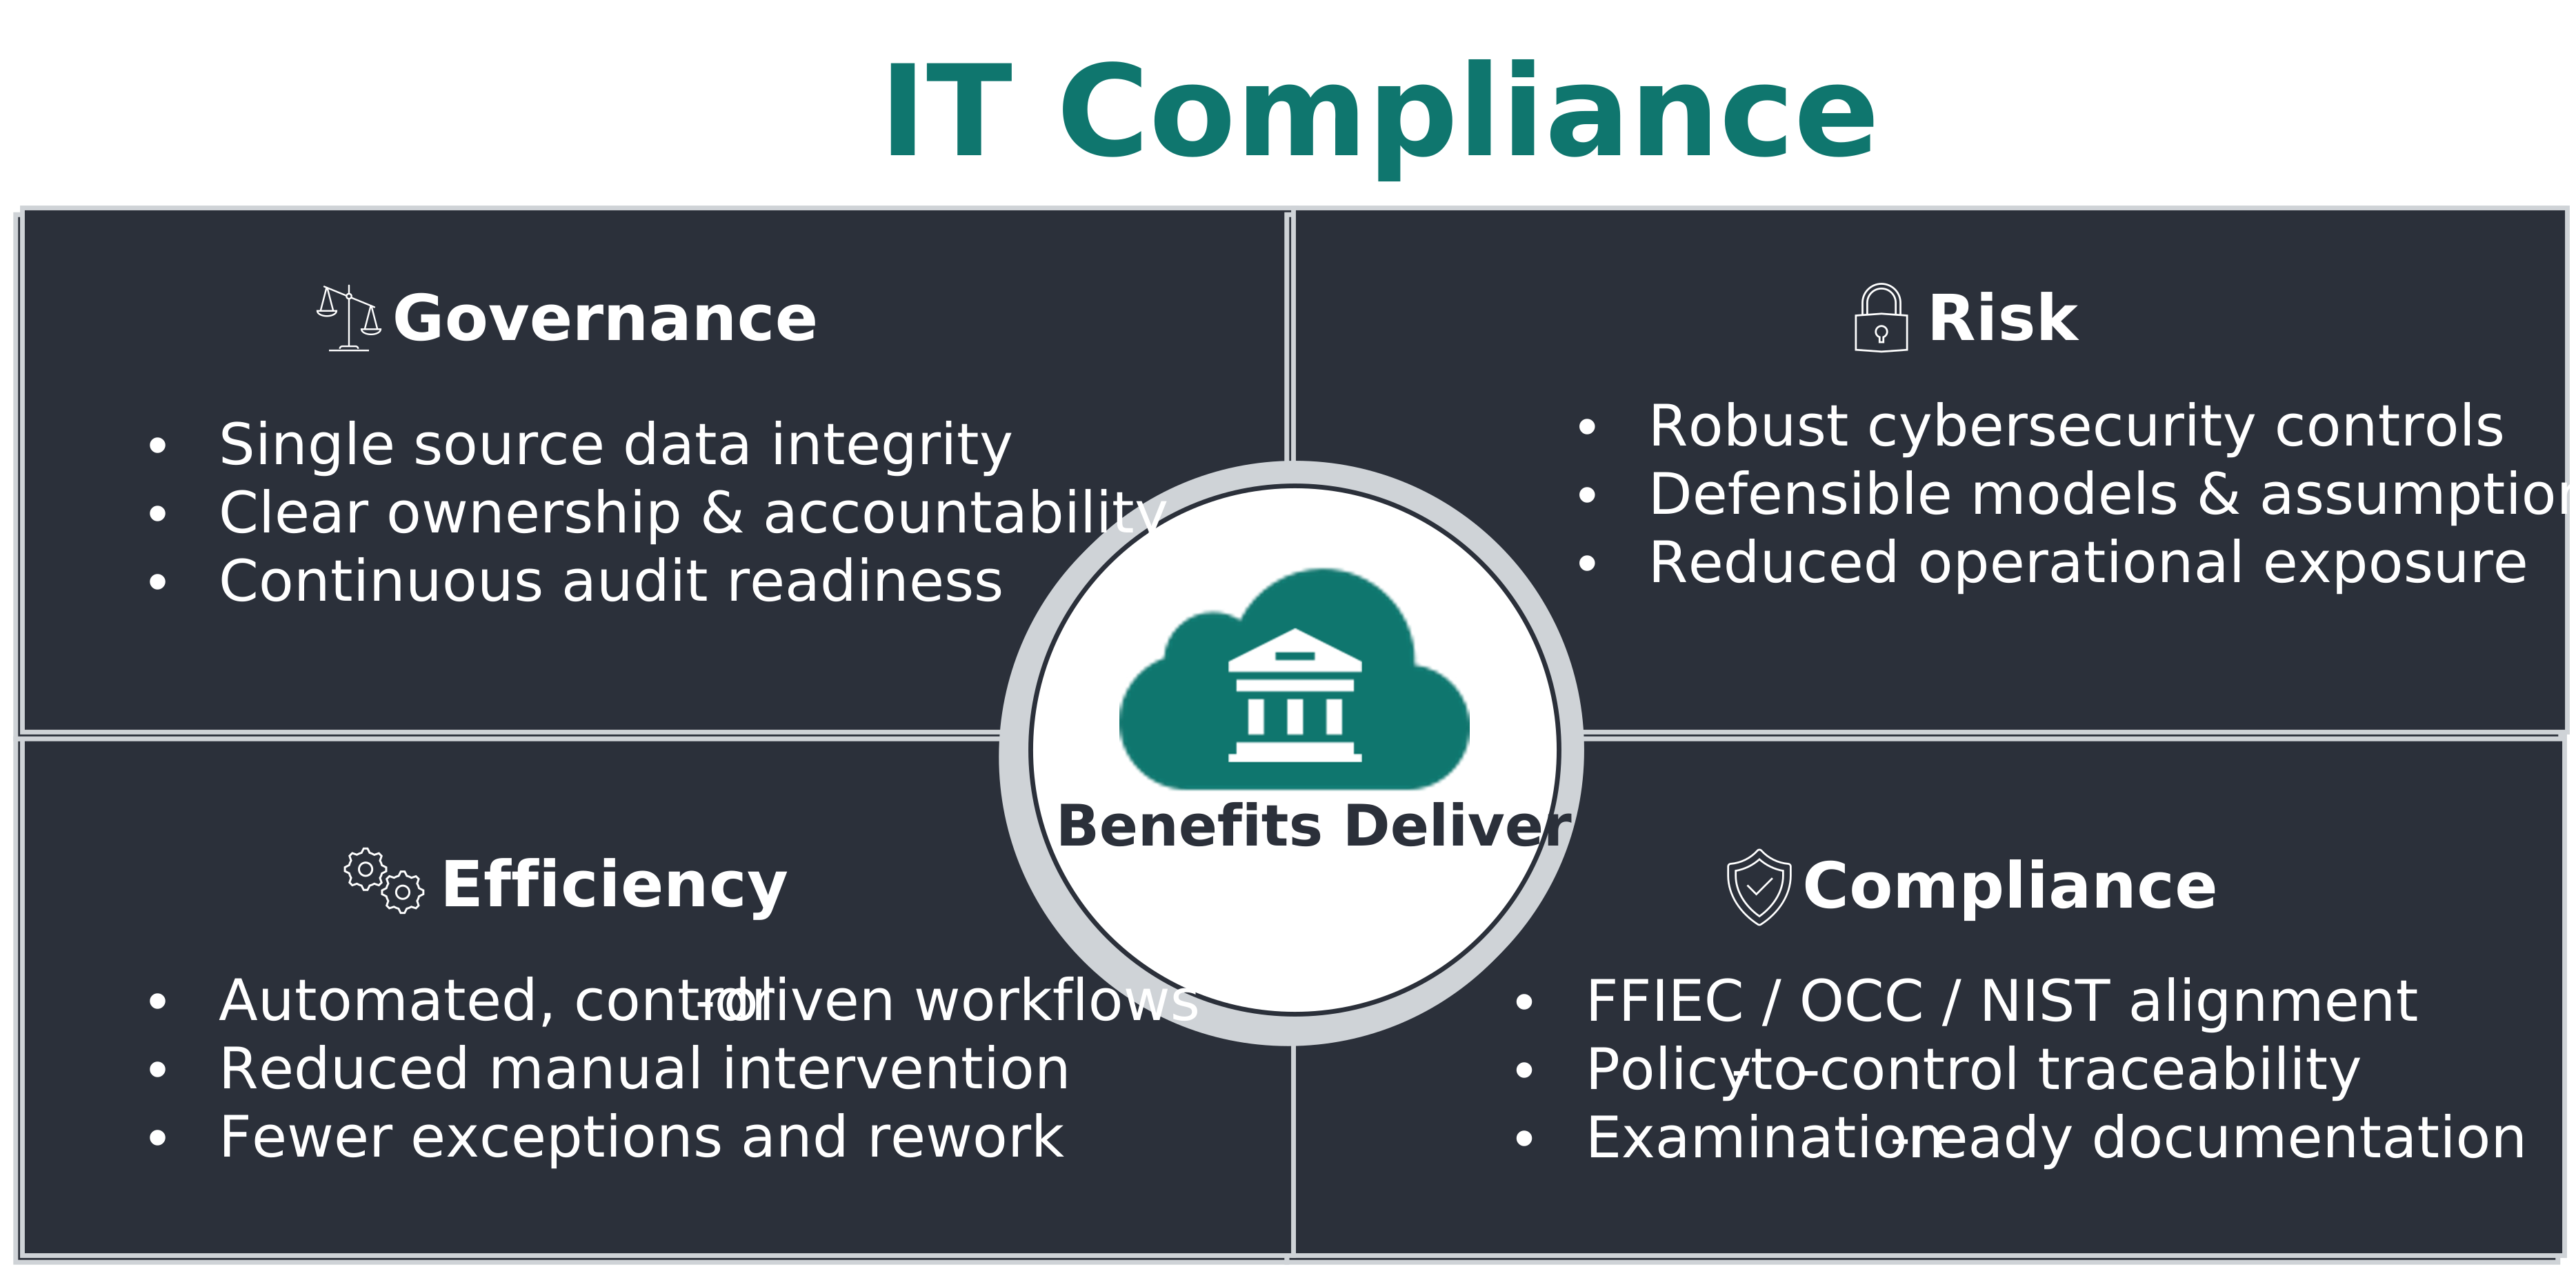
Strong compliance should make the bank run better, not slower. Cicrim helps you reduce redundancy, remove ambiguity, and improve the quality of control evidence through standardized policies, documented workflows, and measurable control outcomes. The result: Clearer governance, faster audits, smoother exams, and lower operational risk.
Our services
Cicrim combines bank IT leadership, controls engineering, and regulatory execution to help you withstand exams, audits, and third-party scrutiny. We build practical, evidence-driven compliance programs across cybersecurity, IT governance, vendor risk, access controls, change management, incident response, and audit readiness, without slowing the business.
IT Governance & Policy
Build a governance program exam teams can follow. Cicrim standardizes your IT policies, procedures, and control ownership so the organization can operate consistently, even through staff changes.
Deliverables typically include an IT governance framework, policy library alignment, RACI ownership mapping, control narrative templates, and board-ready reporting that ties technology risk to business outcomes.
Vendor Risk
Reduce third-party risk and improve examiner confidence with an end-to-end vendor risk program: Due diligence, contracting guardrails, ongoing monitoring, issue management, and reporting.
Cicrim helps you implement repeatable evidence packs for critical vendors, SOC review checklists, control mapping, risk tiering, SLA/BCP requirements, and remediation tracking, so audits stop living in spreadsheets.
Data Protection
Protect customer data and prove it. Cicrim helps you document and operationalize data protection controls across data classification, encryption, retention, logging, DLP, and secure data sharing.
We align controls to your risk profile and regulatory expectations, then build evidence artifacts that hold up in audits: Control narratives, key management documentation, access reviews, and incident-ready logging baselines.
IAM & Access
Tighten access controls across core, digital banking, cloud, and internal systems with a program examiners expect: Least privilege, role definitions, privileged access management, joiner/mover/leaver workflows, and periodic access reviews.
Cicrim builds the end-to-end evidence trail, policies, approvals, review cadence, exception handling, and reporting, so IAM controls are verifiable and repeatable.
IT Audit
Turn IT audits into a predictable process. Cicrim helps you prepare for internal and external IT audits by organizing evidence, aligning controls to scope, and eliminating last-minute scrambles.
We build audit-ready artifacts: Control narratives, testing procedures, evidence maps, remediation plans, and ongoing control monitoring so your team can answer “show me” quickly.
Change Management
Strengthen change governance across core integrations, digital banking, cloud, and internal systems. Cicrim implements change controls that satisfy audit requirements while keeping delivery moving: Approvals, testing evidence, rollback planning, and release tracking.
We help you standardize change categories, emergency change handling, documentation templates, and reporting so changes are controlled, traceable, and defensible.
Incident Response & Resilience
Prepare for the events you hope never happen. Cicrim builds incident response programs with clear runbooks, escalation paths, communications templates, tabletop exercises, and evidence capture so you can demonstrate readiness to auditors and regulators.
We also align business continuity and disaster recovery artifacts, RTO/RPO definitions, testing schedules, vendor dependencies, and recovery evidence, so resilience isn’t theoretical.
Cybersecurity
Cicrim helps banks design and maintain cybersecurity programs that are measurable, testable, and aligned to regulatory expectations. We focus on controls and evidence that reduce risk across endpoints, identity, network, cloud, logging, and vulnerability management.
Deliverables include program governance, control mapping, risk register improvements, security metrics, incident readiness, third-party cyber oversight, and audit-ready evidence that supports exam narratives.
Bank IT Compliance
Cicrim helps banks and credit unions strengthen IT compliance readiness across cybersecurity, vendor risk, access controls, change management, incident response, and audit evidence. We focus on what examiners and auditors actually request: Clear governance, repeatable controls, and defensible documentation, delivered in a way that doesn’t slow the business.
Featured insights
Vendor risk evidence packs: What examiners expect to see
A practical approach to due diligence, SOC review, risk tiering, monitoring cadence, and issue remediation, built for audit and exam defensibility.
IAM & access reviews that don’t fall apart at audit time
How to operationalize least privilege, approvals, privileged access, and periodic recertifications with a defensible evidence trail.
Change management controls for core & digital banking updates
Standardize approvals, testing evidence, emergency changes, and rollback documentation without slowing delivery.
Who do banking organizations need to consider within their compliance?
- Federal Deposit Insurance Corporation (FDIC)
- Office of the Comptroller of the Currency (OCC)
- Federal Reserve Board
- Financial Crimes Enforcement Network (FinCEN)
- Office of Foreign Assets Control (OFAC)
- Consumer Financial Protection Bureau (CFPB)
- Federal Financial Institutions Examination Council (FFIEC)
- National Credit Union Administration (NCUA)
- Securities and Exchange Commission (SEC)
- Financial Industry Regulatory Authority (FINRA)
- Institute of Internal Auditors (IIA)
- State banking agencies such as: