Compliant personalization for community banking: A practical playbook
Feb. 13, 2026 · Authored by Terrence A. Thomas
This playbook outlines a practical way to deliver personalization in digital banking without creating examiner anxiety, by anchoring every experience in explicit consent, explainable decisioning, and audit-ready controls.
Community banks are under pressure to offer the same intuitive digital experience customers get from big-tech platforms, but they must do it inside a different reality: Privacy obligations, fair lending risk, UDAAP concerns, vendor concentration, and model governance expectations that don’t allow black box behavior.
The goal of compliant personalization is not to target harder. It’s to reduce friction, improve service, and increase relevance while maintaining provable consistency across customers and segments. That means your personalization logic needs to be (1) grounded in permissible data, (2) governed like a decisioning system, and (3) observable end-to-end, from data lineage to outcomes.
In this playbook, we break personalization down into a set of controllable building blocks: A use-case catalog, a data-permission map, a decisioning policy layer, a monitoring strategy, and an operating model that clarifies who owns each responsibility across Marketing, Digital, Compliance, Risk, IT and the business.
You’ll leave with a step-by-step implementation path that works even if your bank is on a traditional core, even if your digital stack is vendor-heavy, and even if you are just beginning your AI journey. The focus is disciplined modernization: Measurable outcomes, clear controls, and regulator-safe execution.
Purchase the publication to align personalization, privacy, and model risk management, with implementation-ready checklists and governance templates.
Inside the playbook
A regulator-safe framework for personalization, from permissible data and consent to policy-as-code, explainability, and continuous monitoring.
Use-case catalog: Where personalization is worth the risk
Evaluate service, retention, financial wellness, alerts, and next-best-action journeys with clear permissions, review boundaries, and excluded patterns.
AI-Driven Engagement
Use governed data and AI to improve customer relevance, retention, and measurable relationship outcomes.
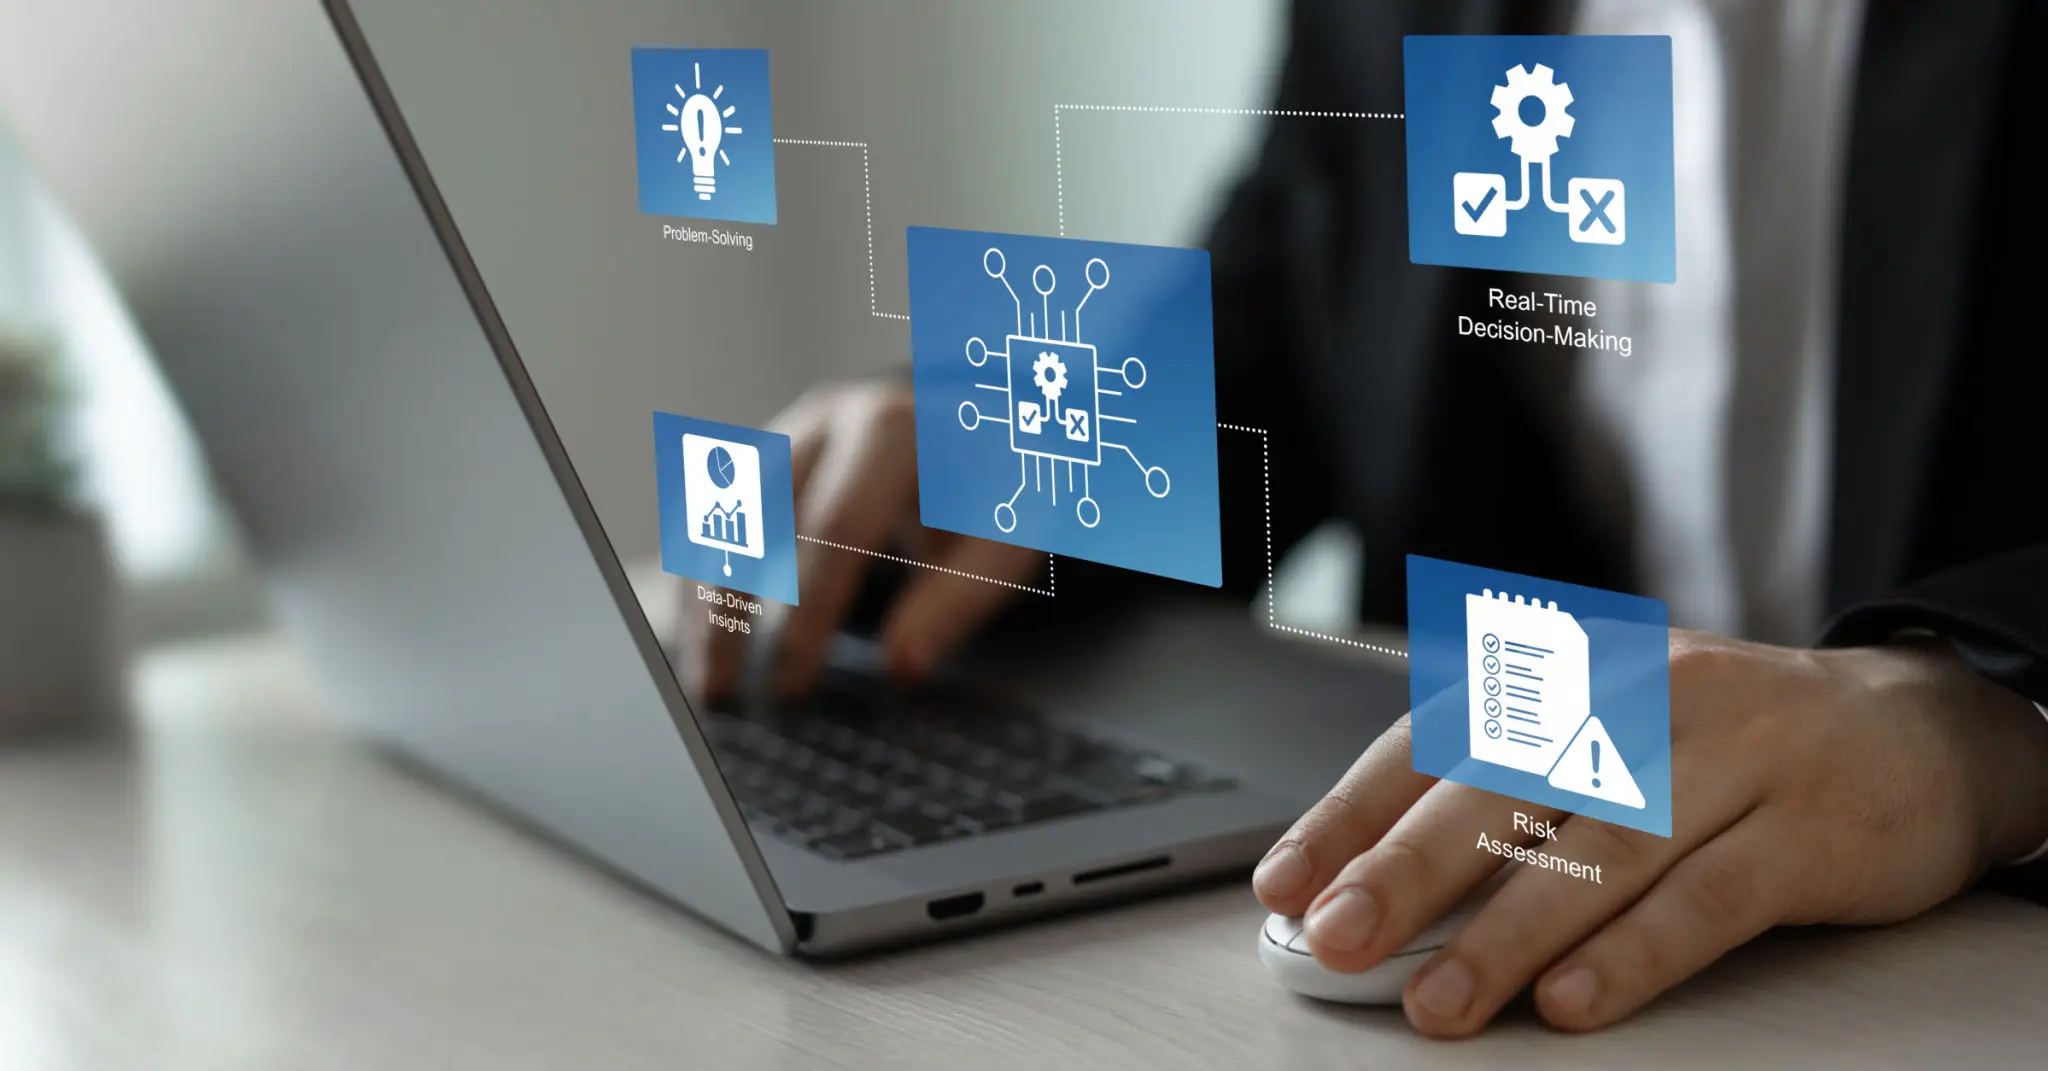
AI-Powered Decisioning
Modernize high-impact decisions with explainability, policy controls, and reviewable evidence.
Digital Lending Platforms
Improve lending speed and consistency while preserving policy discipline, traceability, and human review.
Enterprise AI Stack Design
Build a secure, governed AI foundation that can move from experiment to controlled banking operations.
AI Compliance Solutions
Operationalize responsible AI with governance, monitoring, documentation, and audit-ready controls.
The information provided in this publication is for general informational purposes only and is not intended as legal, regulatory, compliance, or risk-management advice. Each institution’s obligations and risk profile vary based on products, markets, vendors, and applicable laws and supervisory expectations. In specific circumstances, the services of qualified professionals should be sought. Cicrim Consulting does not provide legal advice. Any references to regulatory topics are provided as practical implementation guidance and should be validated with your counsel and compliance leadership.